01Start point: the repository github.com/SkyeChi/sentry-relay.
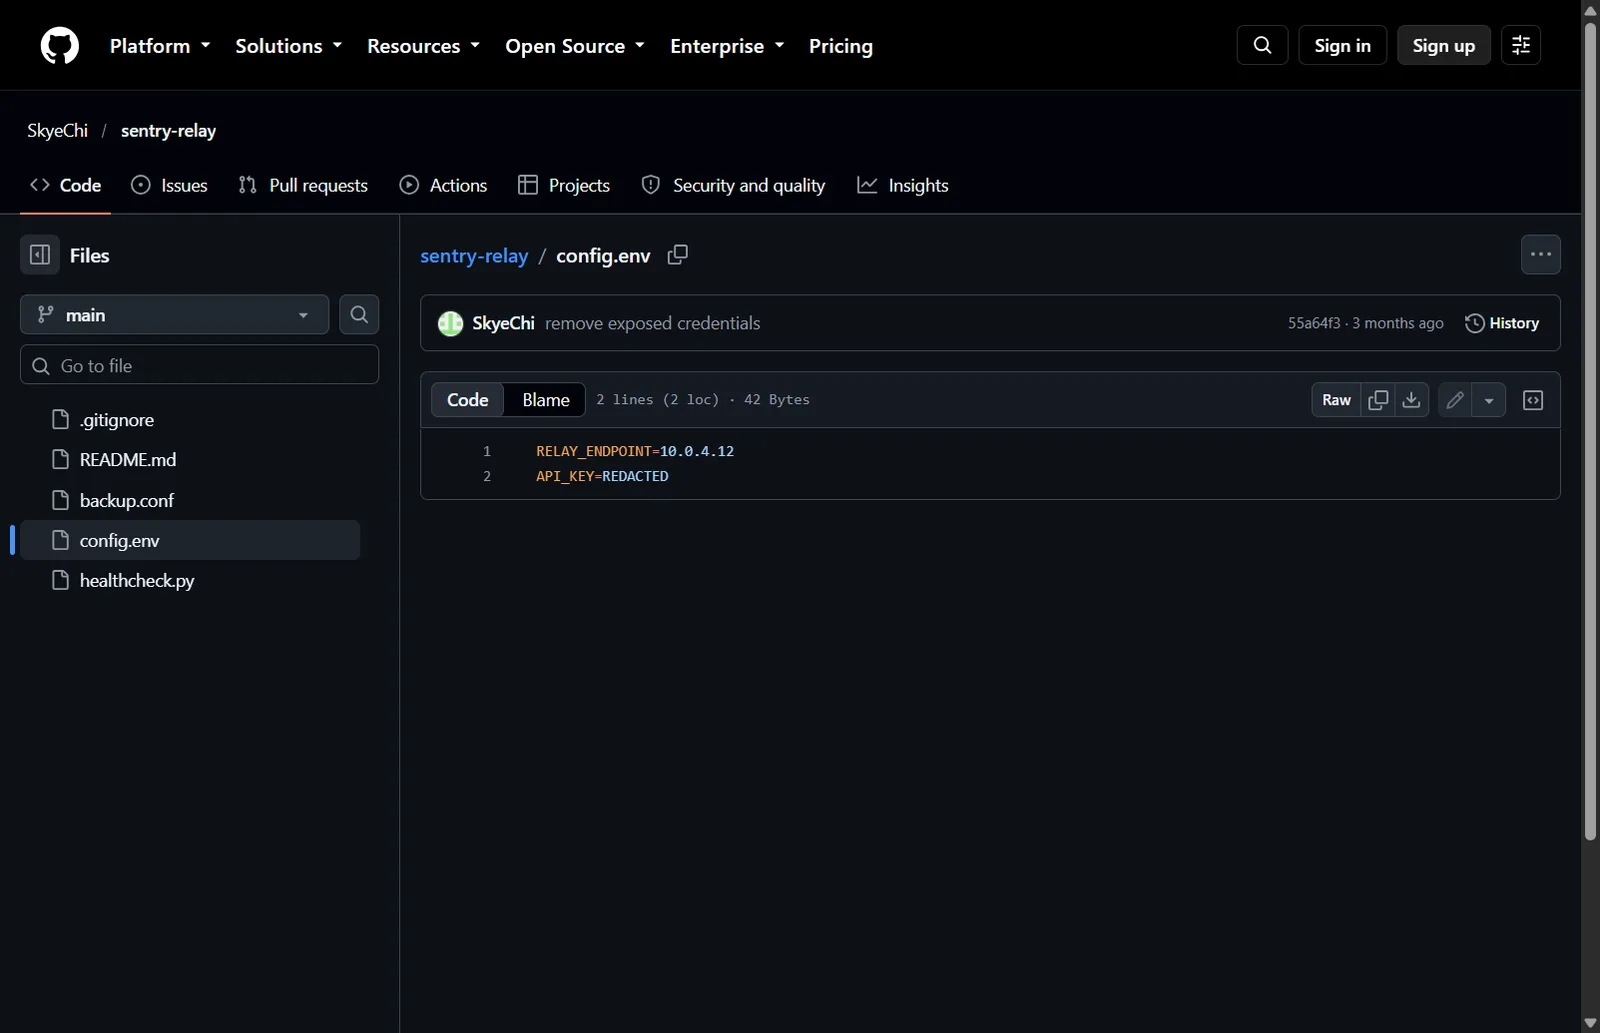
What I found: the current config.env shows API_KEY=REDACTED.
Thinking: a file that has clearly been scrubbed tells you a secret used to be there. Git keeps every version of every file, so the question becomes "which older version still has it?"
config.env today: API_KEY=REDACTED
02Pivot: the commit history.
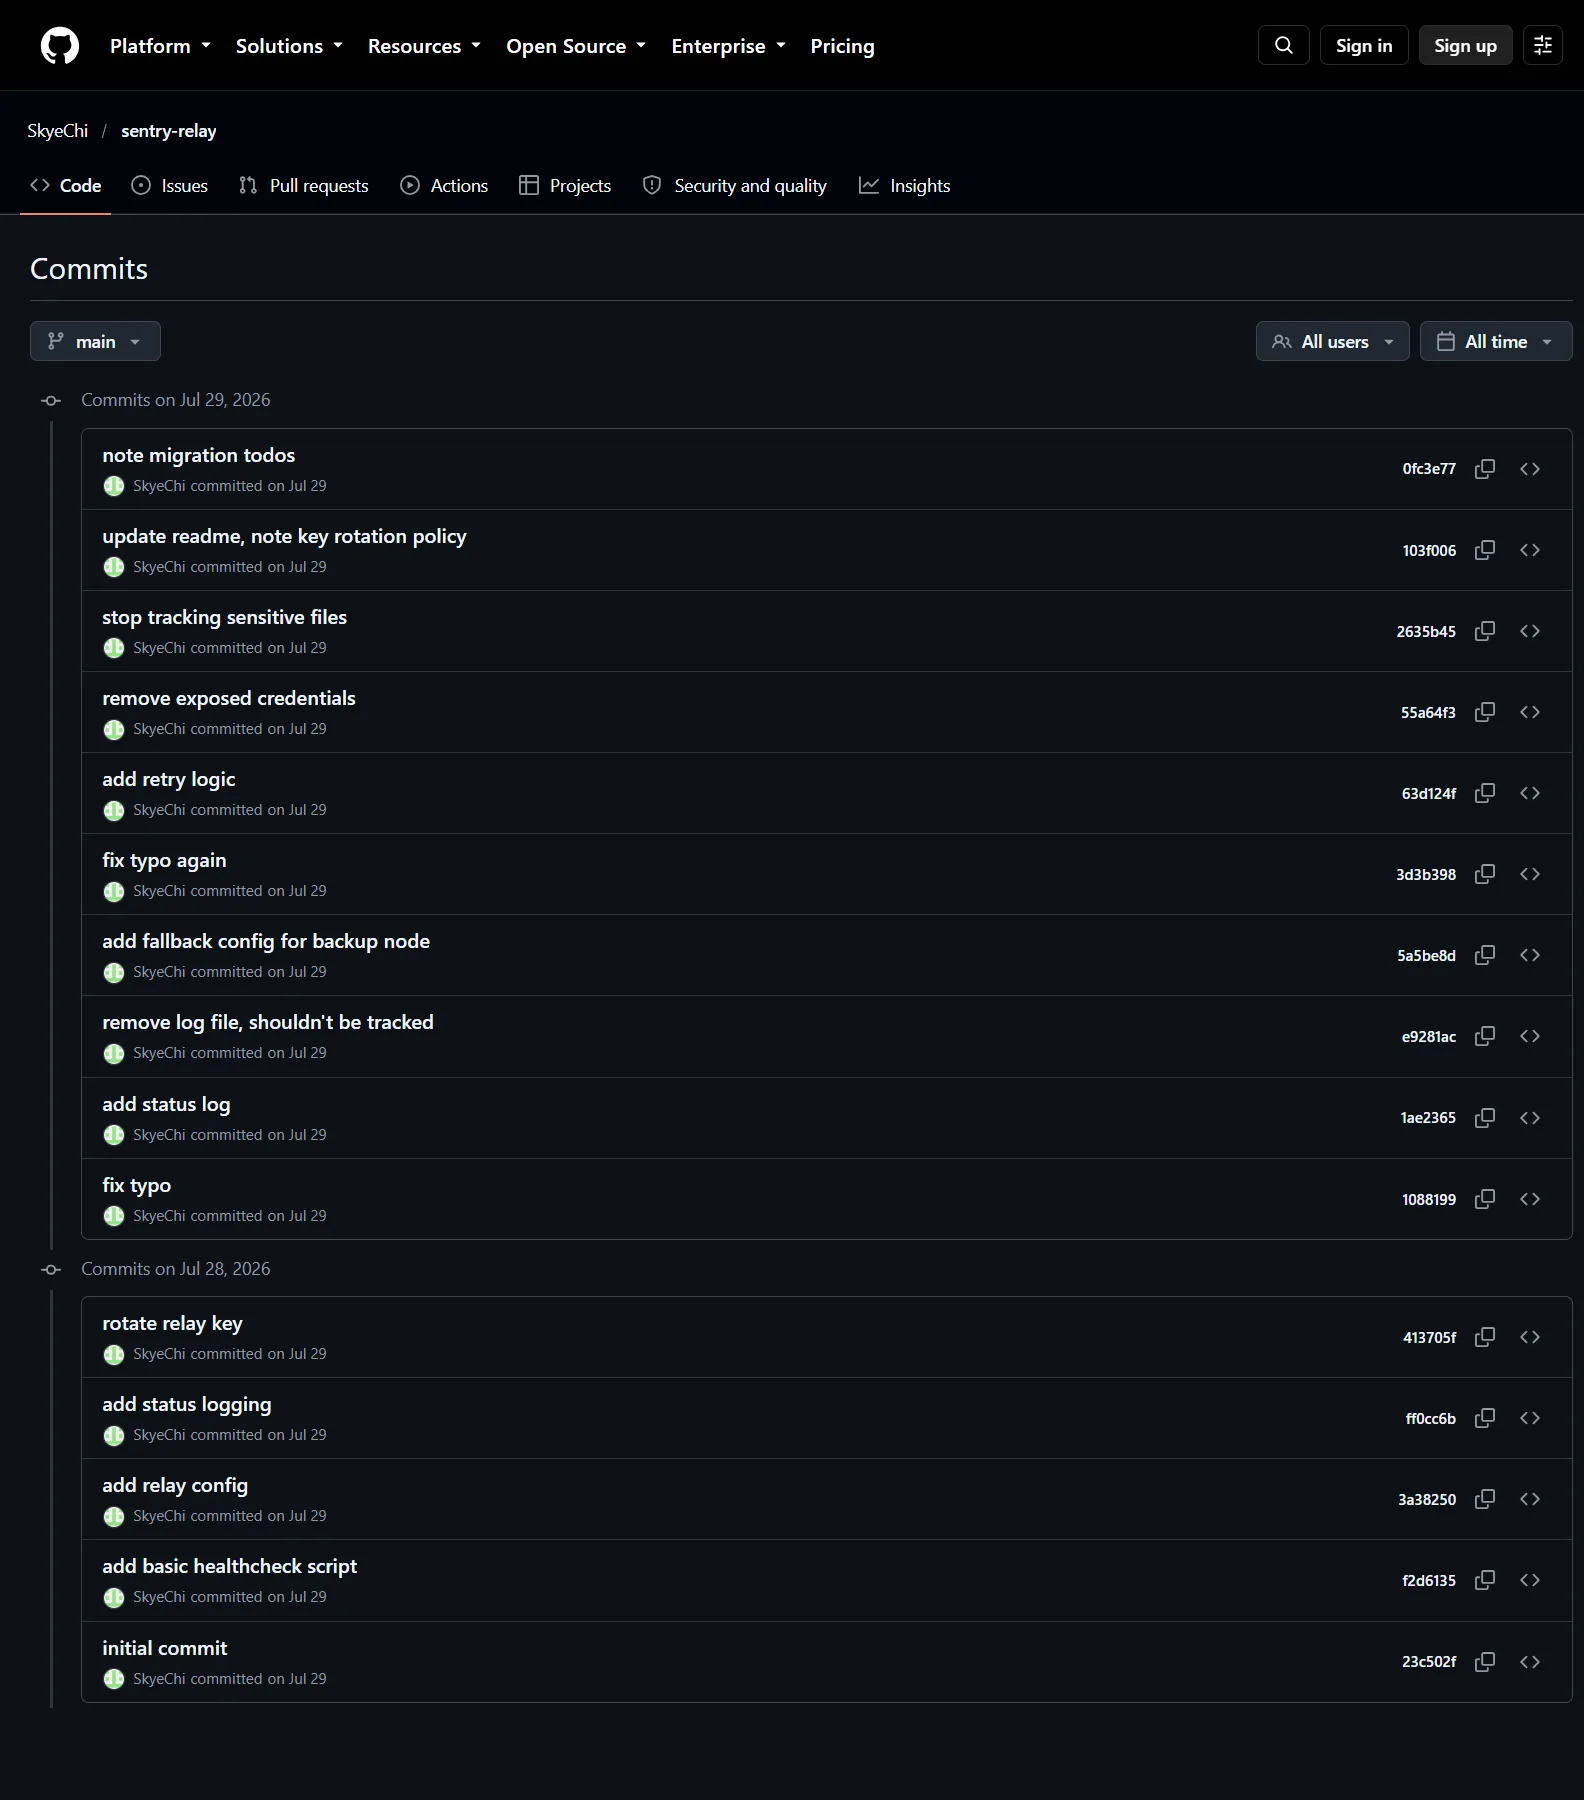
What I did: listed all 15 commits and read the messages.
Result: messages such as "rotate relay key", "remove exposed credentials" and "stop tracking sensitive files".
Thinking: these messages are the developer admitting a leak. They point straight at the commits worth diffing, which saves reading the whole repo.
Commit history
03Pivot: the diffs.
What I did: pulled every commit's patch with gh api and grepped for "PacketCapture{" and "KEY".
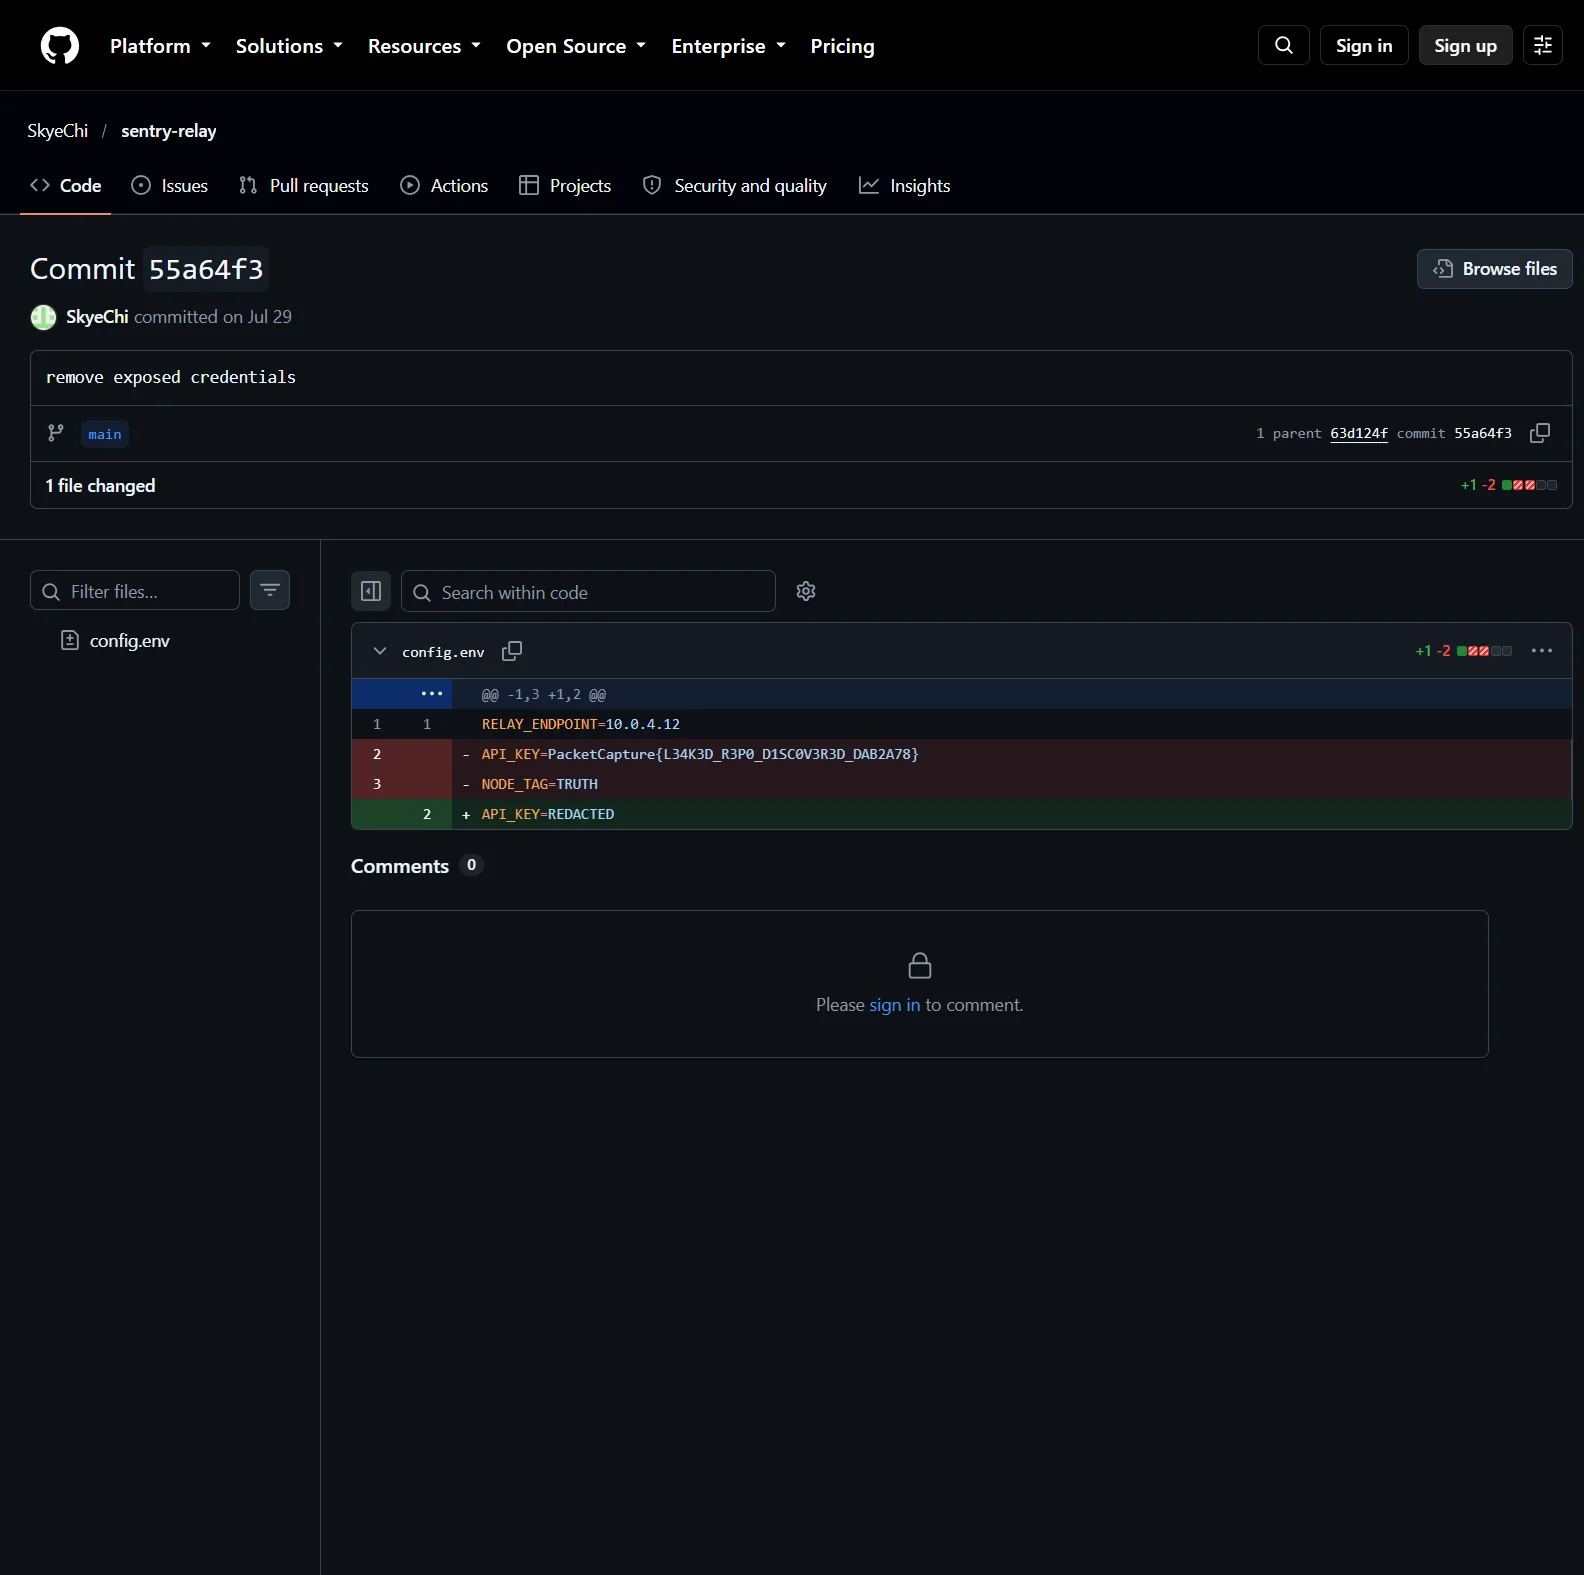
Result: the real key was added in commit 413705f ("rotate relay key") and removed in 55a64f3 ("remove exposed credentials"); the removal diff still shows it in red. Two other flag-shaped values also appear in the history:
Thinking: the two decoys are named after config fields rather than telling a story, which is a common way authors plant wrong answers. The real one reads as a sentence ("leaked repo discovered") and ends with a short hash-like suffix, which is how real flags in this CTF look.
Commit 55a64f3 removing the leaked key
04Verification: submitted the third value and the site accepted it.