Floor1Start

theo@cybersec:~$ whoami

GRCCloud SecurityAI Security

I'm a Computer Science student at De La Salle University, majoring in Network and Information Security. I like the part of security where frameworks meet real systems: mapping controls to ISO 27001 and NIST 800-53, scoring risk, and writing it up so people can actually act on it. Lately I've been building toward cloud security on AWS.

Manila, Philippines · Open to GRC and cloud security internships

Origins

Education

4
De La Salle University seal
Skill

BS CS, major in Network & Information Security.

De La Salle University

BS Computer Science, major in Network & Information Security · Manila · 2024 – 2028

  • Dean's Lister for Terms 1–6, every term to date
  • DOST Merit Scholar, an undergraduate scholarship from the Department of Science and Technology for students in science and technology programs
De La Salle University Department of Science and Technology
2
Power

Senior High, STEM strand. Top 20%.

Elizabeth Seton School

Senior High School · STEM strand

  • Ranked in the top 20% of the STEM batch
  • Excellence Award (With Honors)
  • Annual Excellence Award (With Honors)
  • Outstanding Research Award for senior high research work
  • Oral presenter at the PAREF Southridge Research Congress

The Map

Experience

Security competitions

  1. CTF

    K17 CTF 2026 · top 23%

    UNSW Security Society · Team SlayTheFlagII

    Sep 2026

    CryptoForensicsReversingWebOSINT

    • Placed 152nd of 682 teams in an international jeopardy-style CTF.
    • Solved cryptography, digital forensics, reverse engineering, web exploitation, OSINT and misc challenges.
  2. Information Security Organization, DLSU logo

    CTF

    ISO 2026 CTF · 2nd place

    Information Security Organization, DLSU

    2026

    CryptoLinuxForensicsWebOSINTStego

    • Placed 2nd in ISO 2026 CTF: Uncharted Knowledge.
    • Solved cryptography, OS and Linux, digital forensics, web, metadata analysis, OSINT and steganography challenges.

Read my CTF writeups

Leadership

Student roles alongside my degree. The tags mark what carries into GRC work.

  1. La Salle Computer Society logo

    Leadership · Promoted

    Associate Vice President for Academics

    La Salle Computer Society · promoted from Junior Officer

    Oct 2024 – Sep 2026

    Stakeholder communicationDocumentationScheduling

    • Directed pre-event operations for 10+ academic events: technical talks, exam reviews, publications and coding competitions.
    • Coordinated scheduling, documentation and communication with faculty and partner departments so each event ran on time.
    • Before that, as Junior Officer for Research and Development (Oct 2024 – Sep 2025), helped plan and run the committee's events.
  2. DLSU SPRINT logo

    Leadership

    Associate Vice President for HR Development

    DLSU SPRINT · invite-only leadership organization

    Sep 2025 – Sep 2026

    Team leadershipProgram planning

    • Led member engagement: ran team-building activities and development workshops for 30+ members.
    • Organized 3+ engagement and development initiatives over the term.
  3. Student government

    Executive for Internal Relations

    Computer Studies Government, DLSU

    Sep 2024 – Oct 2025

    Liaison with the Dean's OfficeInternal communications

    • Point of contact between the student government, 10+ student organizations and the Dean's Office, keeping announcements and requests moving.
    • Handled internal communications and email for the College of Computer Studies' student government.
  4. ACM logo

    Organization

    Associate for Activities

    DLSU ACM Student Chapter

    Oct 2024 – Oct 2025

    Facilitation

    • Ran the chapter's general assemblies and lab orientations for members.

Elite Fights

Projects

Likelihood × Impact, 5×5

GRC · Python · In progress

AuditBridge

A compliance mapping and risk register engine.

  • Collects findings from CIS configuration checks, Nmap service scans and read-only web checks in a lab, with severity and evidence.
  • Maps each finding to ISO/IEC 27001, NIST SP 800-53, PCI DSS, SOC 2, OWASP and CIS controls, with the reasoning written down.
  • Scores risk on an explainable 5×5 scale and exports risk registers (CSV/XLSX), compliance report cards and an HTML heat map.
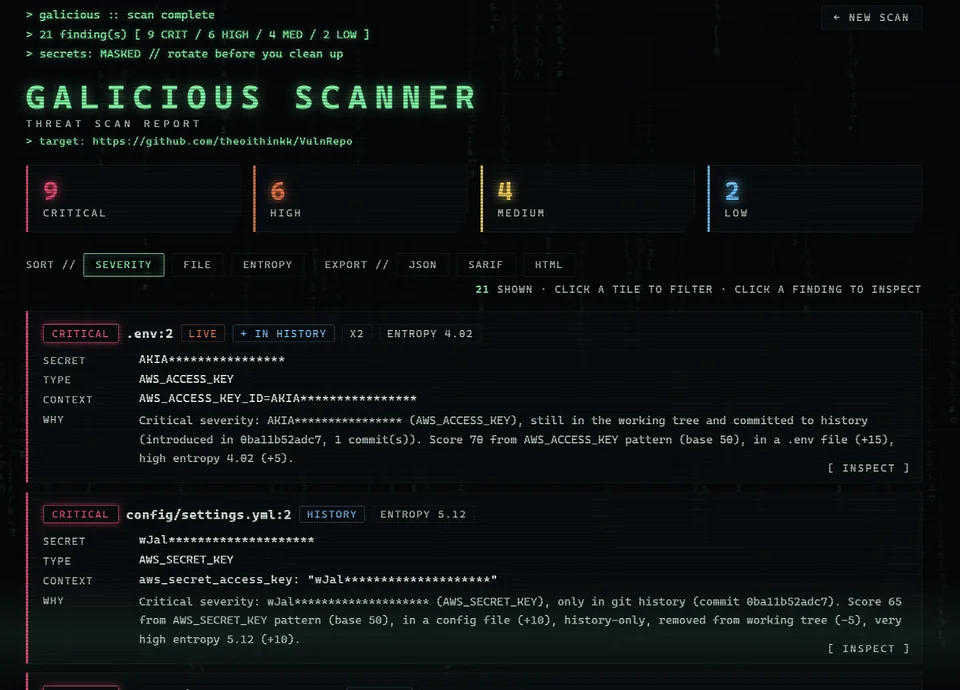
Galicious Secret Scanner report showing 9 critical, 6 high, 4 medium and 2 low findings

Team project · Python · Flask · SARIF

Galicious Secret Scanner

Finds leaked credentials in folders and GitHub repos, including ones deleted from the latest commit but still in Git history.

  • Regex signatures plus a Shannon-entropy check, with an opt-in validity test against AWS STS, GitHub, Stripe and Slack. Every output is redacted.
  • Tested against VulnRepo, a purpose-built repo with history-only secrets and decoys that must not be flagged.
  1. Exposed .git repo
  2. Hardcoded credentials
  3. SQL injection
  4. Cron command injection
  5. Password reuse + sudo
  6. root#

Team VAPT · Jul – Aug 2026 · Nmap · Nessus · Burp Suite · sqlmap

DarkHole V2 penetration test

A black-box internal test of a Linux host and its PHP web app, under a defined scope and rules of engagement.

  • Validated scanner output by hand, then chained five weaknesses into full root access.
  • Co-authored a 39-page findings report: 13 findings (2 Critical, 5 High) with CVSS 3.1 vectors and prioritized remediation.
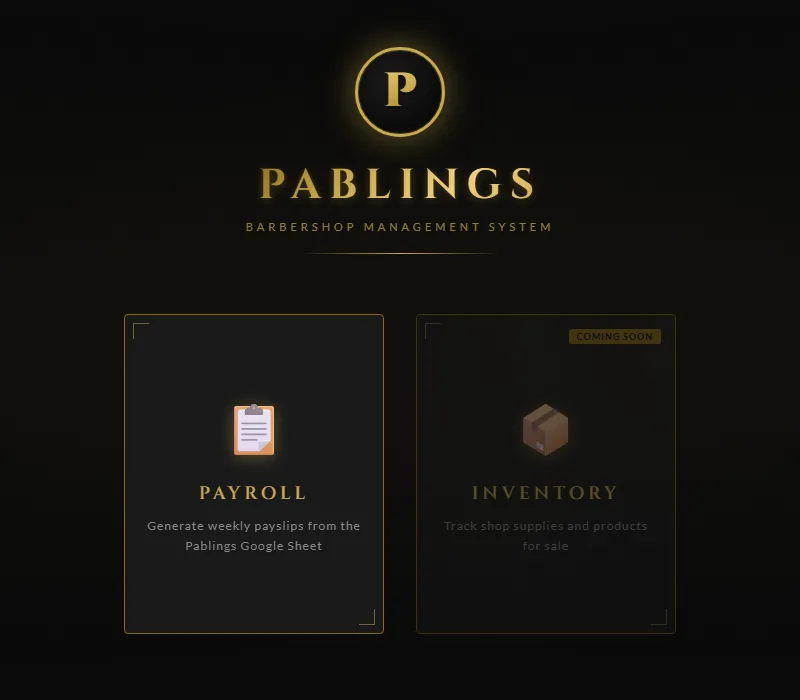
Pablings Barbershop Management System home screen

Real client · Electron · SheetJS

Pablings Payroll

A local-first Windows payroll app built for a working barbershop.

  • Turns the shop's weekly Google Sheet export into commissions, allowances, late deductions and net pay per employee, then exports payslips in the shop's own layout.
  • No cloud and no database, so employee pay data stays on the owner's machine.
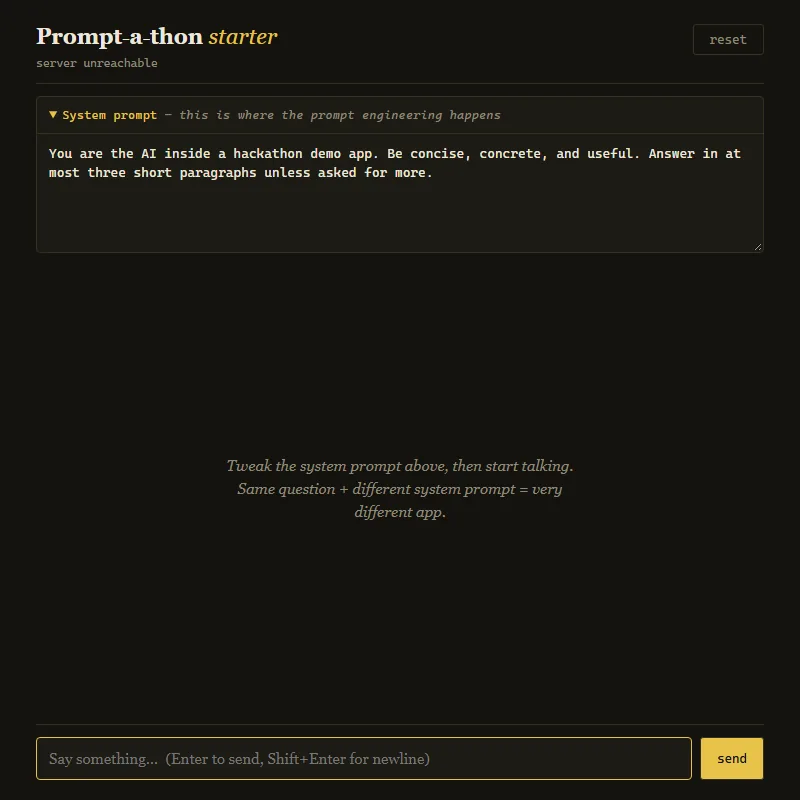
Prompt-a-thon starter chat interface with an editable system prompt

Personal · Node.js · Express · Claude API

Prompt-a-thon practice app

My own starting layout for the LSCS Prompt-a-thon, so competition time goes into the idea instead of setup.

  • Streams Claude API replies to a plain JavaScript chat UI with a live-editable system prompt.
  • Mock mode runs with no API key, and keys stay in an ignored .env file.
CallerCallee INVITE + SDP 180 Ringing 200 OK + SDP ACK RTP audio · RTCP SR BYE

Java · UDP · Networking

VoIP over SIP/RTP

A Java voice-call client built from the protocols up.

  • SIP signaling and SDP negotiation over UDP, RTP audio, and RTCP sender reports every 5 seconds.
  • File, one-way and two-way call modes, with clean teardown between calls.
CatBot mascot, a green robot head

Python · Reinforcement learning

CatBot

A tabular Q-learning bot that learns to catch cats with different movement styles on an 8×8 grid.

  • Evaluated over 20 games against 5 graded cats plus unseen behaviors, with results written to CSV.

Card Rewards

Certifications

All badges on Credly

Skill badges

Course badges from IBM SkillsBuild, separate from the certifications above.

Working towards

Security+CompTIA · next upSoon
AWS Security SpecialtyAWS · the cloud security stepSoon
ISO 27001 Lead Auditor / ImplementerPECBSoon
CISA / CRISCISACA · longer termSoon

Relics

Stack

GRC & Privacy

  • ISO/IEC 27001
  • NIST SP 800-53
  • CIS Benchmarks
  • PCI DSS
  • SOC 2
  • RA 10173 Data Privacy Act
  • 5×5 risk scoring
  • Risk registers
  • Control mapping
  • Policy & SOP drafting

Cloud & AI

  • AWS core services
  • AWS IAM
  • Shared responsibility
  • Claude API
  • GitHub Actions
  • SARIF 2.1.0

Offensive Security

  • Burp Suite
  • Kali Linux
  • OWASP Top 10
  • Nmap + NSE
  • Nessus
  • sqlmap
  • Nikto
  • CVSS 3.1

Languages

  • Python
  • JavaScript
  • Java
  • C
  • SQL
  • PHP
  • Rust
  • HTML
  • CSS
  • Bash

Tools & Frameworks

  • Linux
  • Git
  • GitHub
  • Flask
  • Node.js
  • Express
  • Electron
  • Apps Script
  • Microsoft 365
  • Excel

Codex

Writeups & Notes

CTF solves

Every square is a challenge I solved and wrote up. Hover one to see how, click to read it.

16 flags · 3 events · 5 categories · 69 steps

All writeups on GitHub

Field notes

Short notes on things I learned along the way. Open one to read it.

· Secrets · Git · Cloud

Deleting a secret doesn't un-leak it

Why my secret scanner reads Git history, not just the current files.

Read note

When we built the Galicious Secret Scanner, the most important test wasn't in the latest commit. In our VulnRepo fixture, a "security cleanup" commit moved hardcoded credentials into environment variables. The working tree looked almost clean, but the AWS secret key, a GitHub token and a database password were all still one git log -p away.

The lesson for GRC: the control isn't "remove the secret", it's rotate it, then remove it. Removing it without rotating leaves the likelihood exactly where it was, with a false sense of closure.

In a risk register, a leaked credential that was only deleted should stay open until there's evidence it was rotated.

· Control mapping

One finding, five frameworks

Mapping an exposed .git directory, and why the rationale matters more than the IDs.

Read note

In DarkHole V2, an exposed .git directory was the first step to root. Here's how that one finding maps:

  • OWASP Top 10 (2021): A05 Security Misconfiguration.
  • CIS Controls v8: Control 4, Secure Configuration of Enterprise Assets and Software.
  • NIST SP 800-53 Rev. 5: CM-6 Configuration Settings, CM-7 Least Functionality.
  • ISO/IEC 27001:2022 Annex A: 8.9 Configuration management, 8.4 Access to source code.
  • PCI DSS v4.0: Requirement 2, apply secure configurations to all system components.

Matching IDs is the easy part. What makes a mapping useful to an auditor is the why: the server shipped files it never needed to serve (least functionality), and source code with credentials was reachable by anyone (access to source code). That rationale is what AuditBridge stores next to every mapping.

· Risk

5×5 risk scoring without fooling yourself

The matrix is for sorting risks, not measuring them.

Read note
  • The score is ordinal. Likelihood × impact gives 1–25, but a 12 isn't "twice as risky" as a 6. Use it to rank and prioritize, not to do math.
  • Define the levels before you score. Write down what each likelihood and impact level means for this organization, or two people will score the same risk differently.
  • Score inherent and residual separately. The gap between them is the value of the control, so record the evidence that the control actually works.
  • Explain every score. AuditBridge keeps a one-line rationale next to each rating, so the register still makes sense months later.

· Banking · In progress

Reading BSP Circular 1140 as a student

Notes from preparing for IT risk roles at Philippine banks.

Read note

BSP Circular No. 1140 (2019) sets the Bangko Sentral's expectations for how supervised financial institutions manage IT risk. I'm reading it area by area:

  • IT governance, with oversight from the board and senior management
  • The IT risk management process: identify, measure, control, monitor
  • Information security
  • IT operations, projects and outsourcing to third parties

What stands out so far: expectations scale with how complex an institution's IT is, and accountability sits with the board, not only the IT team. These notes are a work in progress, so read the circular itself for anything you rely on.

The Boss

Contact

Open to GRC, information security and cloud security internships. Based in Las Piñas City, Philippines.